Morgan Wagner · 6 October 2026
Exploring Data Compliance Challenges in Emerging Digital Content Ecosystems
Emerging digital content ecosystems encompass platforms that deliver interactive media, AI-generated works, virtual reality experiences, and decentralized user contributions, and these systems generate vast quantities of personal and behavioral data that trigger compliance obligations under multiple overlapping frameworks. Researchers note that data moves continuously between creators, algorithms, and global audiences, which creates friction points around consent management, cross-border transfers, and retention limits. In October 2026 several jurisdictions plan to activate updated enforcement mechanisms that target real-time content personalization, and those changes require operators to reassess their current data handling pipelines.
Core Components of Modern Content Ecosystems
Content ecosystems now integrate generative AI tools that synthesize user inputs into new media assets, decentralized networks that store fragments across nodes, and immersive environments that capture biometric signals during sessions. Data from these activities includes prompts, viewing histories, spatial coordinates, and inferred preferences, and each category falls under distinct regulatory definitions in different regions. Observers point out that traditional consent mechanisms struggle when content mutates after initial collection, because downstream uses may exceed the scope originally disclosed to individuals.
Regulatory Pressures Across Regions
Authorities in the European Union continue to refine guidance on automated decision-making, while Canadian officials enforce updates to the Personal Information Protection and Electronic Documents Act that emphasize accountability for algorithmic outputs. Australian regulators, through the Office of the Australian Information Commissioner, have issued directives on data minimization in digital advertising ecosystems, and similar rules appear in draft legislation across Asia-Pacific markets. Figures from enforcement actions in 2025 reveal that fines for inadequate cross-border safeguards exceeded previous annual totals, which prompts platforms to map data flows more granularly.
Those who track policy calendars expect additional clarity in October 2026 when certain provisions of updated digital services regulations take effect, and organizations must prepare documentation that demonstrates lawful bases for processing data used in content recommendation engines. Studies from academic institutions indicate that fragmented rules across borders raise operational costs, because each jurisdiction imposes unique requirements for data subject access requests and breach notifications.
Technical and Operational Hurdles
Implementing granular consent controls becomes complicated when content ecosystems rely on third-party libraries for rendering or analytics, and companies must verify that every vendor maintains equivalent safeguards. Data minimization principles collide with the need to retain training datasets for model improvement, and technical teams therefore explore techniques such as federated learning and differential privacy to reduce identifiable elements while preserving utility. Research indicates that decentralized storage solutions introduce new variables around jurisdiction because nodes may reside in territories with conflicting legal demands.
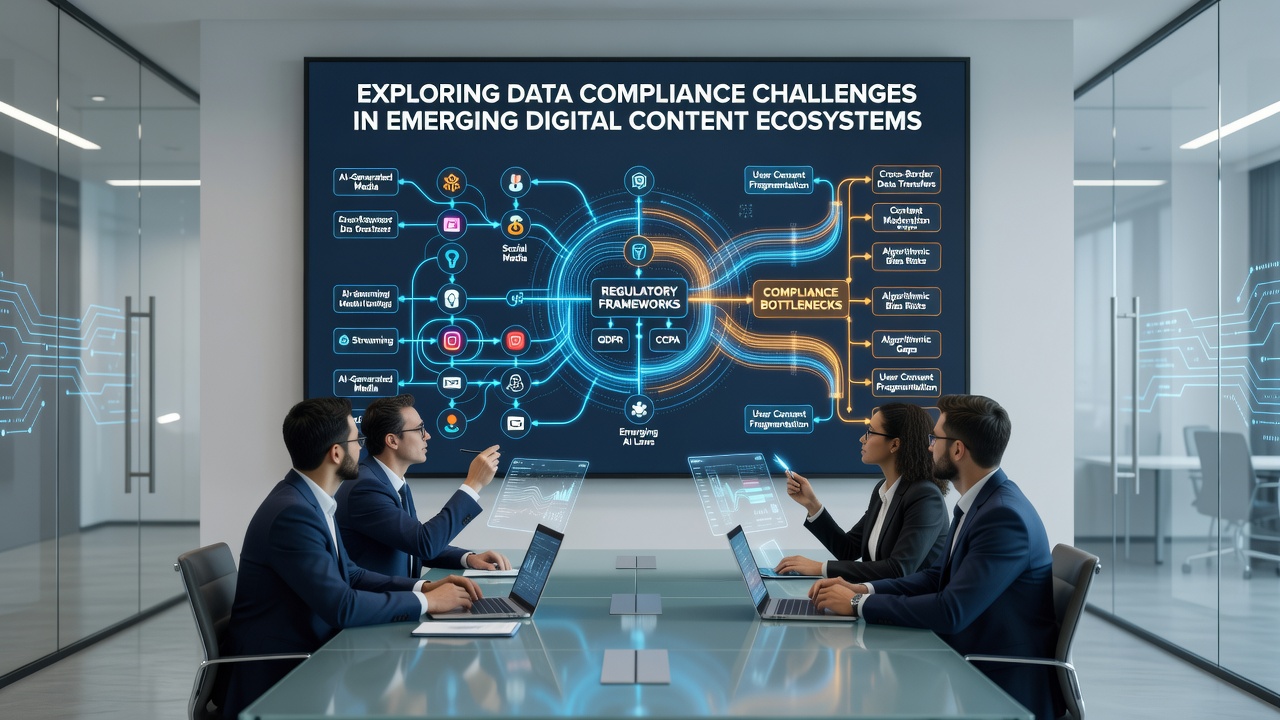
Security requirements extend beyond encryption at rest, because real-time content delivery networks must protect data in transit across multiple hops, and any single weak link can expose user profiles. Operators also confront challenges in auditing AI-generated outputs for unintended leakage of personal information that was embedded during training phases. One study revealed that synthetic media sometimes reproduces identifiable traits from source material even after scrubbing attempts, which complicates compliance verification.
Industry Responses and Emerging Practices
Trade associations have published frameworks that encourage standardized metadata schemas for consent signals, and several platforms now embed machine-readable preference tokens that travel with content assets. According to reports from international organizations, collaborative initiatives between regulators and technologists have produced pilot programs for automated compliance checking tools that scan pipelines before deployment. These efforts demonstrate measurable reductions in policy violations during controlled tests, although scaling remains an ongoing task.
Companies that operate across multiple ecosystems frequently adopt unified data governance platforms capable of applying jurisdiction-specific rules dynamically, and such systems rely on continuous monitoring rather than periodic audits. Evidence from recent implementations shows that early integration of compliance checks during the design phase lowers remediation expenses compared with retrofitting existing infrastructure.
Conclusion
Data compliance in emerging digital content ecosystems centers on aligning technical architectures with evolving legal obligations across borders, and organizations continue to refine processes that address consent, minimization, and security simultaneously. As October 2026 approaches, updated enforcement timelines will test the adaptability of current systems, and stakeholders will track whether coordinated standards can reduce duplication while maintaining individual protections. The interplay between innovation in content creation and regulatory oversight will shape operational strategies for years ahead.